Governance & Compliance
Establish strong security governance frameworks and ensure regulatory compliance to protect data, reduce risk, and strengthen organizational resilience.
Overview
Organizations today face increasing regulatory pressure and evolving cyber threats that require structured governance and compliance frameworks. Atlas United's Governance & Compliance service helps businesses establish effective security policies, manage risks, and align with national and international standards such as the NCA Essential Cybersecurity Controls, PDPL, ISO 27001, NIST, and CIS Controls. Through assessments, policy development, and compliance monitoring, Atlas United enables organizations to strengthen cybersecurity governance, maintain regulatory readiness, and build a resilient security posture that protects critical assets and supports business growth.
Customer challenge
Organizations often struggle to maintain effective security governance, manage complex regulatory requirements, and enforce consistent policies across IT environments.
Regulatory complexity
Multiple regulations make compliance and policy management challenging.
Lack of security governance framework
Lack of structured frameworks limits effective cybersecurity oversight and risk management.
Inconsistent security policies
Security controls differ across departments, increasing operational risk.
Audit & compliance readiness
Poor documentation and control management make regulatory audits difficult.
Strengthen governance & regulatory readiness
Improved governance framework
Regulatory compliance support
Standardized security policies
Risk management enhancement
Audit readiness
Improved security accountability
Our solutions
Atlas United Governance & Compliance services help organizations implement security frameworks, enforce policies, manage risks, and meet national and international compliance requirements.
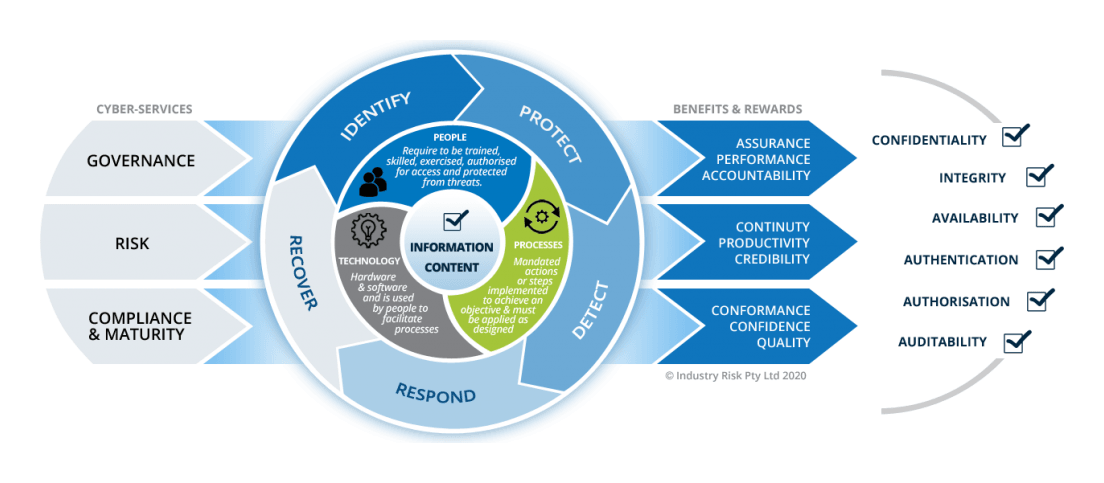
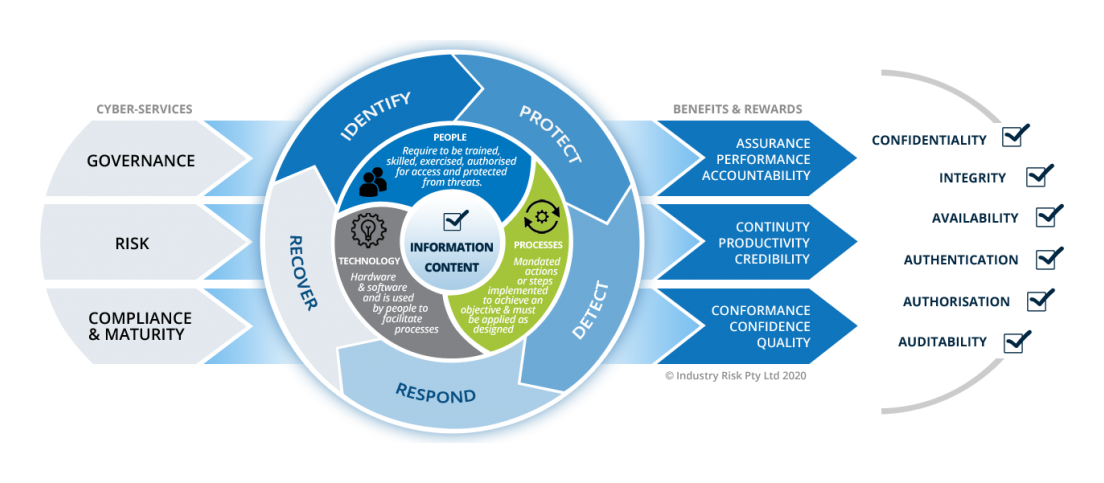
- Implement cybersecurity governance frameworks aligned with NCA ECC, ISO, NIST, and CIS standards.
- Assess compliance posture and identify security gaps.
- Establish security policies, procedures, and risk management controls.
Highlights
- Security governance framework development
- Compliance assessment & gap analysis
- Policy & risk management implementation
Where Governance & Compliance makes the difference
Financial services
Ensure compliance with financial security regulations and strengthen risk governance.
Healthcare
Protect sensitive patient data while meeting healthcare regulatory requirements.
Government & public sector
Implement governance frameworks to secure critical national systems.
Technology & enterprises
Standardize security policies to maintain consistent governance and manage risks.
Why choose Atlas United Governance & Compliance
Expert governance advisory
Atlas United cybersecurity experts help design governance frameworks aligned with global security standards and regulatory requirements.
Compliance readiness assessments
Evaluate current security posture and identify gaps before regulatory audits or certification programs.
Risk-based security approach
Focus on prioritizing high-impact security risks to improve governance efficiency and operational security.
Continuous compliance improvement
Ongoing advisory and monitoring help organizations maintain compliance and strengthen security maturity over time.
Want more?
Explore our other managed security services designed to strengthen your cybersecurity posture.
Cyber Defense Center (SOC)
24/7 monitoring, threat detection, and incident response across enterprise environments.
Penetration Testing (Risk Identification)
Identify vulnerabilities and security weaknesses that could impact compliance and governance frameworks.
Threat Intelligence
Gain insights into emerging threats and risks that may affect regulatory compliance.
Cloud Security (CNAPP / CSPM)
Ensure cloud infrastructure follows governance policies and compliance requirements.
Security Awareness
Educate employees on security policies, compliance requirements, and cyber risk management practices.
Technical Assessment
Evaluate security architecture and controls to strengthen governance and compliance readiness.
Digital Forensics and Incident Response (DFIR)
Investigate incidents, identify root causes, and support regulatory reporting and remediation.
Let's talk about your business security strategy
Have a question or need more information? Get in touch and our cybersecurity experts will assist you.